Zero Trust thrives on information, so position your group to maximise the collection and breakdown of this useful resource. Be ready to continually check methods and networks to confirm the success of your Zero Belief initiative. Diligently follow both least-privilege and least-functionality entry to your most precious resources. These accesses management the user’s capability to view, navigate, change, or execute the contents of a protected file system. This follow is taken into account important to maintaining a Zero Trust environment, and tons of really feel even this isn’t strict enough to keep out malicious invaders. Customers are granted community access upon displaying two or extra forms of identification based mostly either on what they know (password), possess (physical merchandise like token or cellphone), or inherently comprise (fingerprint or retina).
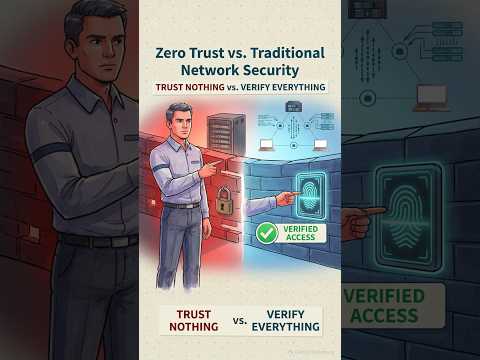
Always Verify
With zero belief architecture in place, nevertheless, you probably can apply safety insurance policies to validate identities of users and workloads. Conduct thorough knowledge discovery and classification to grasp what information requires safety and then apply the appropriate security controls based on sensitivity ranges. Defining high-, moderate- and low-impact assets may help you higher slim your focus and assets round zero trust tactics.
Making Use Of the least privilege precept means giving users solely the minimal entry they need to do their jobs. This reduces the danger of unauthorized access and limits the harm from compromised accounts. Continuous monitoring means all the time checking consumer actions and community site visitors https://www.techtraders.in/ to find something uncommon or potentially dangerous. Utilizing superior analytics and machine studying helps rapidly spot and respond to security issues. Micro-segmentation breaks the community into smaller, separate parts, which limits the unfold of threats within the network.
Zero-trust verifies user identification and system safety regardless of connection location or network. Workers access solely the purposes needed for his or her roles rather than the complete corporate community. Identification governance ensures constant policy enforcement across cloud purposes, on-premises techniques, and hybrid environments.
Enhance Cloud Surroundings Entry Management
As Quickly As in, hackers nonetheless have steady entry until they log off or the system logs them out. Lack of executive sponsorship ends in insufficient price range allocation, inadequate useful resource commitment, and an absence of organizational precedence. Customers and administrators require coaching on new instruments, processes, and duties to ensure the profitable adoption of those adjustments.

Ongoing Upkeep And Coverage Updates
By separating workloads and implementing strict entry controls, Netflix reduces the danger of threats shifting sideways and improves its overall safety. The term “Zero Trust” in cybersecurity was coined by John Kindervag, a former analyst at Forrester Analysis, in 2010. Since then, networks have turn out to be more advanced, threats have grown more subtle, and safety leaders have largely purchased into the idea that it’s time to assume past conventional perimeter-based safety fashions.
This prevents attackers who’ve infiltrated the system from gaining access to valuable knowledge. Importantly, these phases aren’t only required once – they should be cycled through constantly as organizations secure (at most) several apps at a time. This guidance displays a legacy view of microsegmentation, where months of planning, manual configuration, and time-consuming ongoing management are inevitable. It is not a complete alternative or a one-time deployment that’s then in place for the lifetime of the community.
- Begin by thoroughly evaluating present safety infrastructure, identifying gaps, and understanding present safety capabilities.
- This apply is considered essential to sustaining a Zero Trust setting, and many feel even this isn’t strict sufficient to keep out malicious invaders.
- Now it’s time to decide who you’ll let in, and what they may be succesful of do once inside.
- Using superior analytics and machine studying helps shortly spot and reply to safety issues.
- IAM uses features like MFA and Single Sign-On (SSO) to confirm users and determine the level of entry they will be granted.
What’s Ztna?

We must take away trust from the fashionable surroundings, verifying everyone and every little thing regardless of location. By implementing zero trust, organizations create a safer surroundings that protects against a variety of threats and supports their enterprise aims. Endpoints have to be verified to verify each is being managed by the best person. Endpoint verification strengthens a zero belief security method as a result of it requires each the consumer and the endpoint itself to present credentials to the community.
It surfaced in 2010 when a Forrester analyst named John Kindervag introduced new battle strains in cybersecurity. He recognized data wasn’t neatly behind protected walls anymore, and the only method to maintain it secure was in a trust-free surroundings. Google’s adoption and implementation of Zero Trust methodologies created a wider curiosity. In April 2020, Google lastly launched its Beyond Corp Remote Entry product, which is based on the Zero Belief approach they implemented for almost a decade. With the rise of cellular enterprise environments, cloud service, IoT, and bring-your-own-device policies, the nature of security has modified dramatically.